Design access controls and traceable application behaviour around your security and operational requirements.
What we can help you build
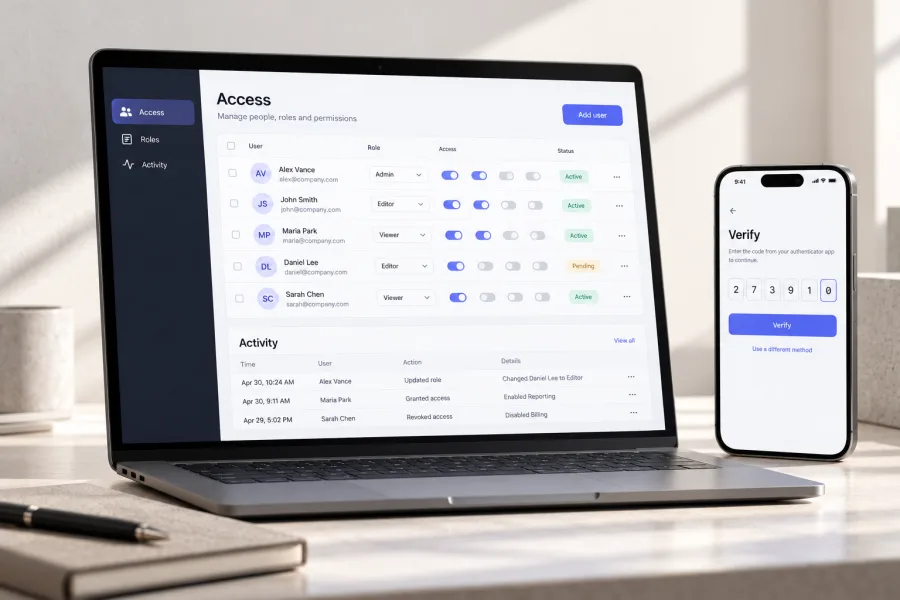
- Role-based access control
- Multi-factor authentication
- Audit trails and permission reviews
- Requirements-led security controls
Turn access requirements into testable behaviour
A business application may allow staff to create requests, supervisors to approve them and administrators to manage accounts. We map these responsibilities into permissions enforced by the backend, then design how the interface explains the available actions. MFA and session controls are selected around the account risks and recovery process.
How controls are reviewed
An access-control review checks both permitted and rejected actions, including direct API calls and access to another organization's records. Audit requirements define which events are captured, who can inspect them and how sensitive information is handled. Security controls support your requirements; they do not establish regulatory certification or replace an independent assessment.
What to bring to the first conversation
Bring the role matrix, sensitive data categories, existing authentication setup and applicable requirements identified by your stakeholders. We can scope an access review or a focused control implementation.
Software controls can support a compliance program. Certification, legal obligations and independent audits require the appropriate qualified reviewers; this service does not promise certification or blanket compliance.